
How they actually work, where they break, and why DAST plus source intelligence is pulling ahead
API security approaches
1. Inline WAF / “API‑Runtime Protection”
How it works: Terminate TLS, parse every request, apply ML‑backed rules, block on the wire.
When it helps: Quick win for a single internet‑facing gateway.
Hidden costs & deal‑breakers
- Needs full reverse‑proxy insertion, every edge, every region.
- Does not fail open; if the proxy dies your API is offline.
- Blind to internal and service‑to‑service traffic (usually >80 % of calls).
- $‑per‑TPS adds up fast once you go beyond the public ingress tier.
2. Traffic Mirroring & eBPF/Sidecar Telemetry
How it works: Clone packets with VPC Traffic Mirroring or an eBPF sidecar; ship raw streams to the vendor’s cluster for deep analysis.
When it helps: You need flow visualisation for a short forensic project.
Hidden costs & deal‑breakers
- Up to 50 TB/month duplicated traffic for a mid‑size estate, storage and egress bills dwarf the licence.
- Full payloads (tokens, PHI, PCI) leave your boundary → automatic GDPR & HIPAA red flag.
- Non‑K8s workloads? Service mesh disabled? Agent install blockers halt rollout.
3. Spec Linting (“Swagger Hygiene”)
How it works: Run an open‑source linter against OpenAPI docs; flag inconsistent verbs, auth gaps, data‑type mismatches.
When it helps: Mature external developer programme with pristine specs.
Hidden costs & deal‑breakers
- Finds spec defects, not actual vulns.
- Useless for the ~70 % of endpoints that have no Swagger at all.
- Zero runtime signal: business‑logic flaws, auth bypass, broken object‑level auth never surface.
4. Legacy DAST via HAR Playback
How it works: Developers record traffic (HAR), feed it to a scanner that replays requests with OWASP Top‑10 payloads.
When it helps: One‑off pre‑prod scan of a single service, when you have the people to script a clean capture.
Hidden costs & deal‑breakers
- Continuous coverage impossible without end‑to‑end test harnesses, dev teams rarely have bandwidth.
- Priced per‑scan or per‑endpoint, so portfolios with 1000+ micro‑services explode the budget.
- Still bound to existing documentation (or HAR) → shadow & zombie APIs remain invisible.
5. “Contract‑Aware” DAST (Swagger‑Driven)
How it works: Import Swagger, crawl endpoints, fuzz parameters, report exploitable findings.
When it helps: Teams disciplined enough to ship perfect specs before code hits staging.
Hidden costs & deal‑breakers
- Requires accurate, complete spec first. In reality, most prod APIs are undocumented.
- Misses internal gRPC or event‑driven surfaces that aren’t HTTP‑REST.
6. Hybrid Source Intelligence + DAST (NightVision)
How it works:
- Source intelligence reads supported REST frameworks to generate an OpenAPI spec of the routes they declare, with no dev tickets, no sidecars and no data egress.
- The generated spec seeds a DAST engine that runs authenticated, stateful tests against the discovered endpoints: injection (SQL, command, template), cross-site scripting, server-side request forgery, path traversal, CORS and security-header misconfiguration, and JWT validation flaws.
- Request-level findings preserve HTTP evidence; supported source-discovered API findings can add file and line context in GitHub Security Alerts.
Why it clears the enterprise bar
- Fail‑open: All scanning happens out‑of‑band; production traffic path untouched.
- Zero data residency risk: Only metadata/spec leaves the estate; no tokens, no PHI.
- Beyond the spec: Routes your code declares but your documentation missed, including undocumented ones, go into the API scan.
- Dev adoption: Three CLI commands; no reverse proxies, no sidecars, no HAR gymnastics.
- TCO: One platform covers discovery and exploit‑level testing; no second vendor for visibility, no seven‑figure packet‑capture bills.
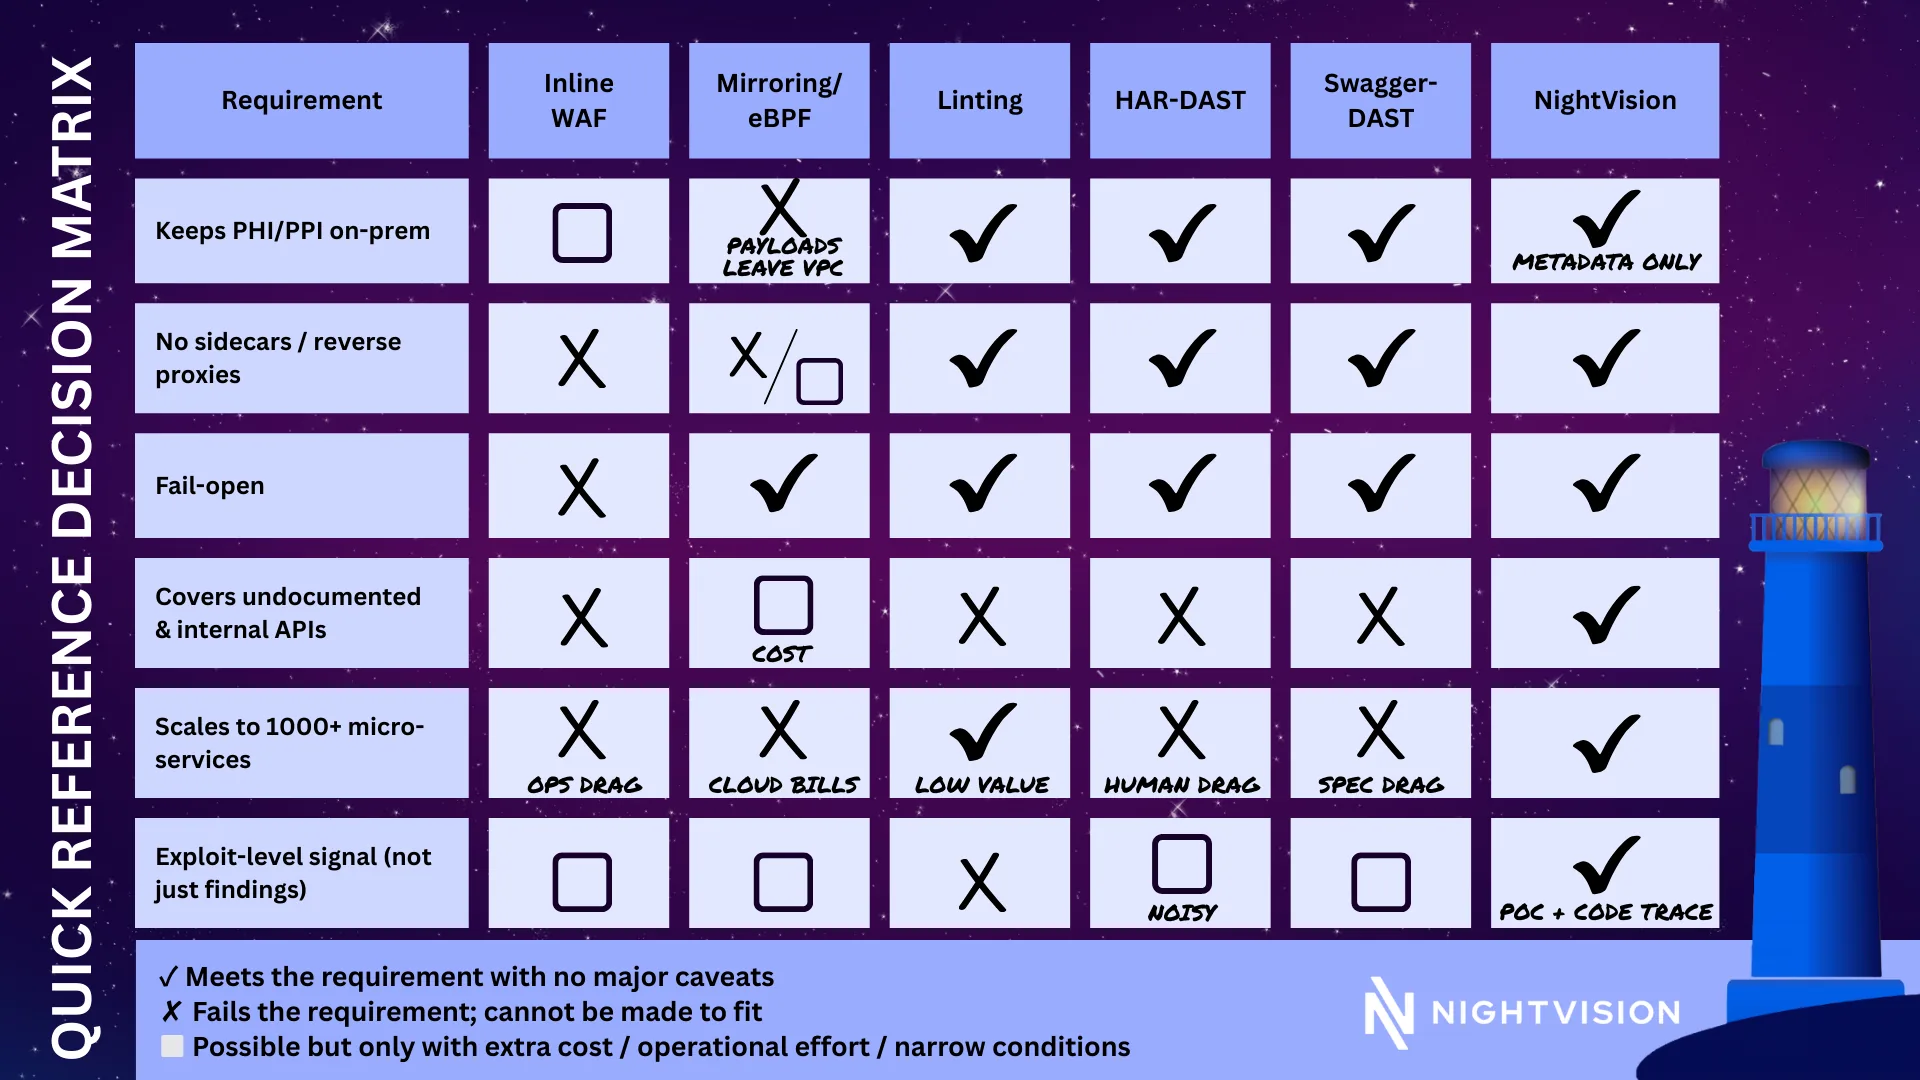
What to Ask Every Vendor
- Show me the full data path. Where do tokens and payloads land?
- Describe your failure mode. Does production traffic drop if your sensor dies?
- How do you handle un‑documented endpoints? If the answer is “ask devs to write Swagger,” keep walking.
- What’s the monthly AWS bill for a ___ Gbps workload? If they won’t estimate, you already know.
- How long from git clone to first exploitable finding? Time‑to‑signal is the best reality check.
NightVision’s DAST plus source intelligence alternative
NightVision’s approach to API security pairs DAST that challenges APIs directly through synthetic attacks with source intelligence that tells the scan which routes exist.
- First, NightVision’s API discovery from source code uses source intelligence: it reads how supported REST frameworks declare routes and generates an OpenAPI file from them, locally and deterministically; no LLM reads your code. The file comes from the code rather than from a separately maintained Swagger file, and it is human-readable, so it can also serve as a catalog of the recognized routes for audits, compliance reviews or due diligence.
- Using that file, NightVision’s DAST scanner sends attack payloads to the listed API endpoints to test them for exploitable vulnerabilities.
NightVision’s standard DAST check set also includes AI endpoint security testing: it tests whether an endpoint backed by a language model can be steered into calling an attacker’s server or reading your cloud metadata service, and reports those only with proof.
Source intelligence maps the routes inside an app you already know about. To find the apps themselves, app discovery starts from your domain to find the web apps and APIs tied to it, including ones nobody onboarded, and shows why each one is listed. You confirm which ones are yours and turn them into scan targets.
These are the critical distinctions between NightVision’s strategy and other approaches to API security. Other methods protect against the effects of bad API behavior. Used collectively, those methods may be reasonably effective, yet only up to a point. NightVision gives your developers the tools, the information, and the support they need to stop the bad behavior altogether. Learn more in our guide to next-generation API security testing.
Bottom Line
Most “API‑security” products still guard only what they can see, the documented, internet‑facing slice of your estate. Meanwhile, threat actors happily pivot through the internal, the forgotten, and the mis‑documented.
NightVision flips that problem on its head by building the missing map of recognized routes from code, then testing those routes live, without rerouting traffic, siphoning data, or drowning teams in false‑positive noise.
When the boss asks why you’re not buying a proxy, an eBPF agent farm, and a separate discovery tool, you can copy‑paste:
“Those stacks either break our data‑residency rules, fail closed, or leave 80 % of our estate untested. NightVision tests the routes our code declares, with exploit‑level proof and zero production drag, at a price that isn’t 50 TB of mirrored traffic per month.”